
Authorized Physical Action in Vehicle Manufacturing
Automotive plants depend on coordinated equipment, repeatable production sequences, and clear responsibility for every intervention. Physical AI and Artificial Intelligence of Things (AIoT) can connect machine-state observations and production rules to a defined physical response, provided the action stays within an approved operating boundary. In OEM vehicle manufacturing, that boundary may involve a fixture, a station-level mechanism, or a controlled adjustment to production equipment.
An authorized-action workflow does more than issue a command. It establishes what equipment may be affected, why an action is appropriate, who or what is permitted to approve it, how the command is handled, and how the resulting state is confirmed. The implementation must be adapted to the plant’s equipment, controls architecture, operating procedures, and safety requirements.
Contact OEMNex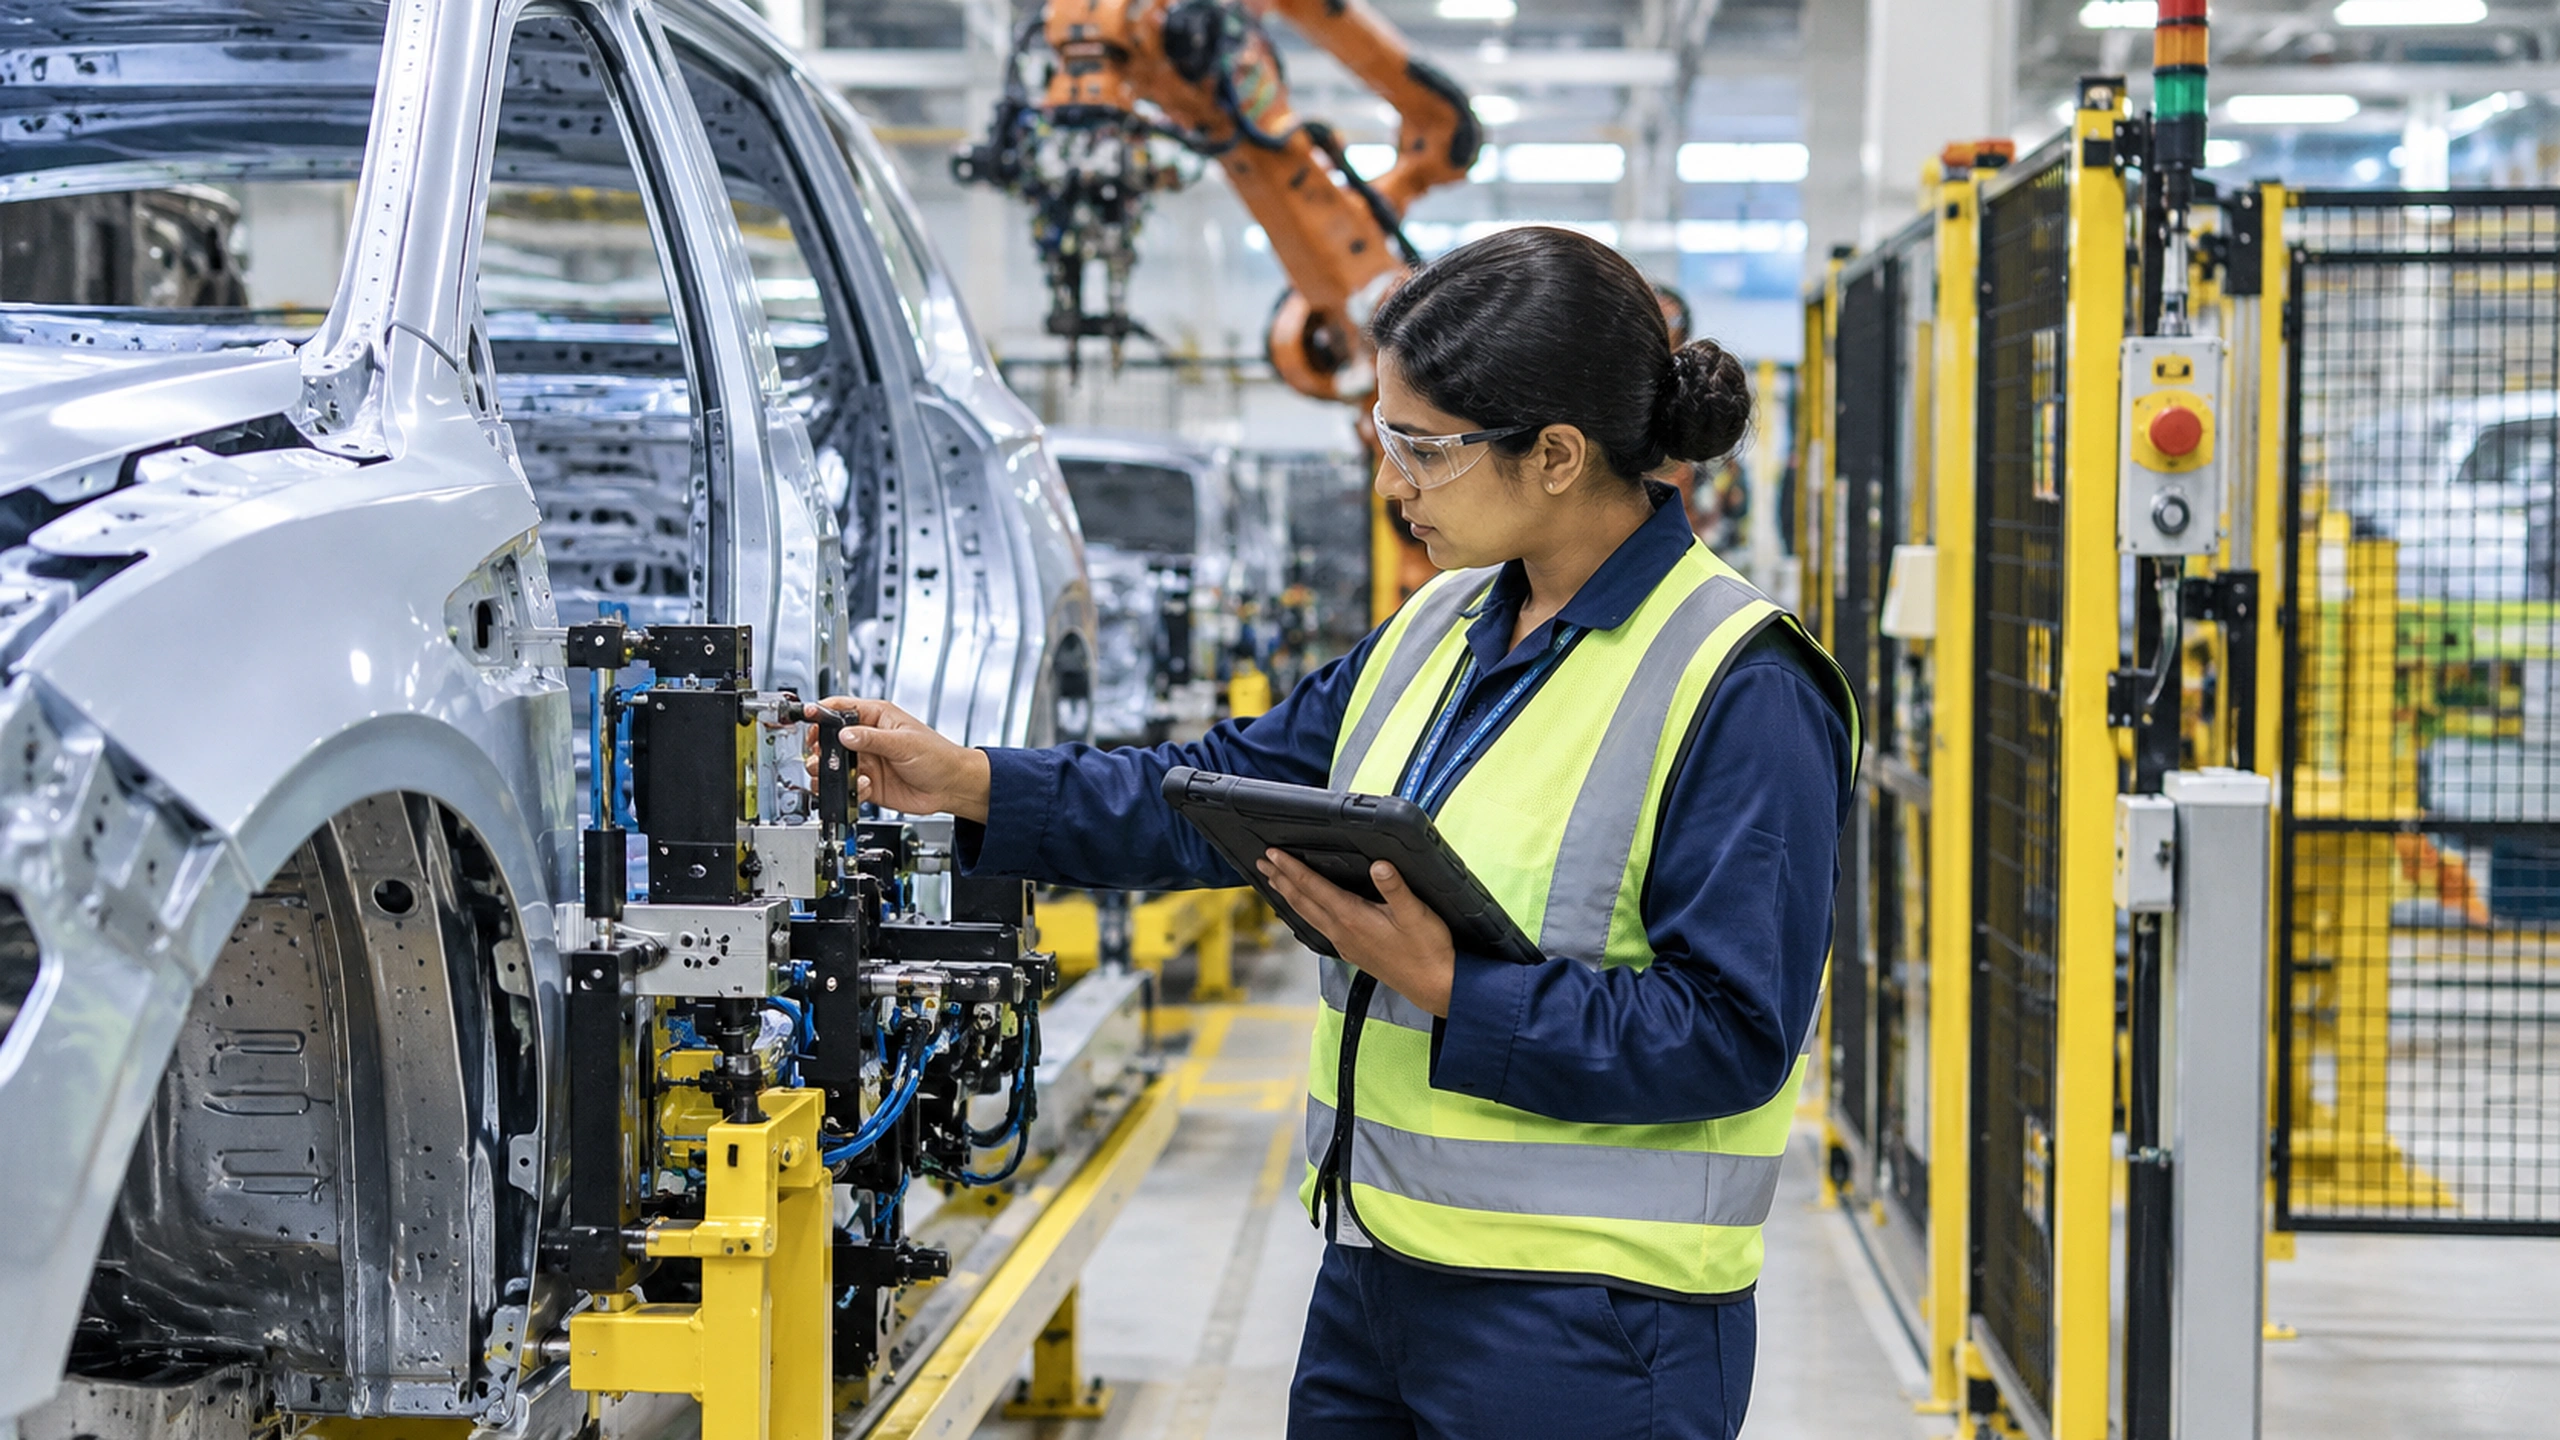
Example: A bounded adjustment at an assembly station
Consider an illustrative body-in-white or final-assembly station where a fixture or positioning mechanism needs a limited adjustment before the next vehicle body or component can proceed. Equipment sensors and controller status provide the current operating context. A decision function checks the station state against approved process rules and the permitted adjustment range. If required conditions are not met, the request is held for operator review or rejected rather than passed to the equipment.
The exact target, adjustment range, and command interface must be defined by the plant’s controls and manufacturing engineering teams. The example describes a workflow to evaluate, not a claim that OEMNex currently controls a specific fixture or production line.
From observation to controlled execution
A practical design separates the information used to make a decision from the mechanism that executes the action. The Physical AI and AIoT workflow can be organized into the following stages:
- Observe: collect relevant equipment status, sensor readings, station state, part or vehicle identity where needed, and event timestamps. Check freshness and data quality before using an observation.
- Evaluate: apply documented process rules or an evaluated model to determine whether the requested action fits the current operating conditions. Record the decision basis and any uncertainty.
- Authorize: verify the required role, approval state, interlocks, and operating limits. The approval model may require a human confirmation, depending on the action and site procedures.
- Dispatch: send a bounded request through the designated controller or equipment interface. Keep supervisory requests separate from low-level control loops and independent protective functions.
- Acknowledge and verify: record the controller response, then compare the requested state with independent evidence such as a subsequent position or sensor reading. An acknowledgment alone does not prove that the physical action completed.
- Recover: if authorization fails, the command is rejected, a timeout occurs, or observed state differs from the target, follow the defined stop, hold, escalation, or recovery procedure.
Decision inputs and operating constraints
The required inputs depend on the selected station and action. They may include controller state, fixture or actuator position, process step, vehicle or component identity, sensor quality, equipment availability, and the current production interlocks. Inputs should have defined units, timestamps, validity checks, and ownership. Stale, conflicting, or incomplete observations should trigger a hold or escalation when they affect safe execution.
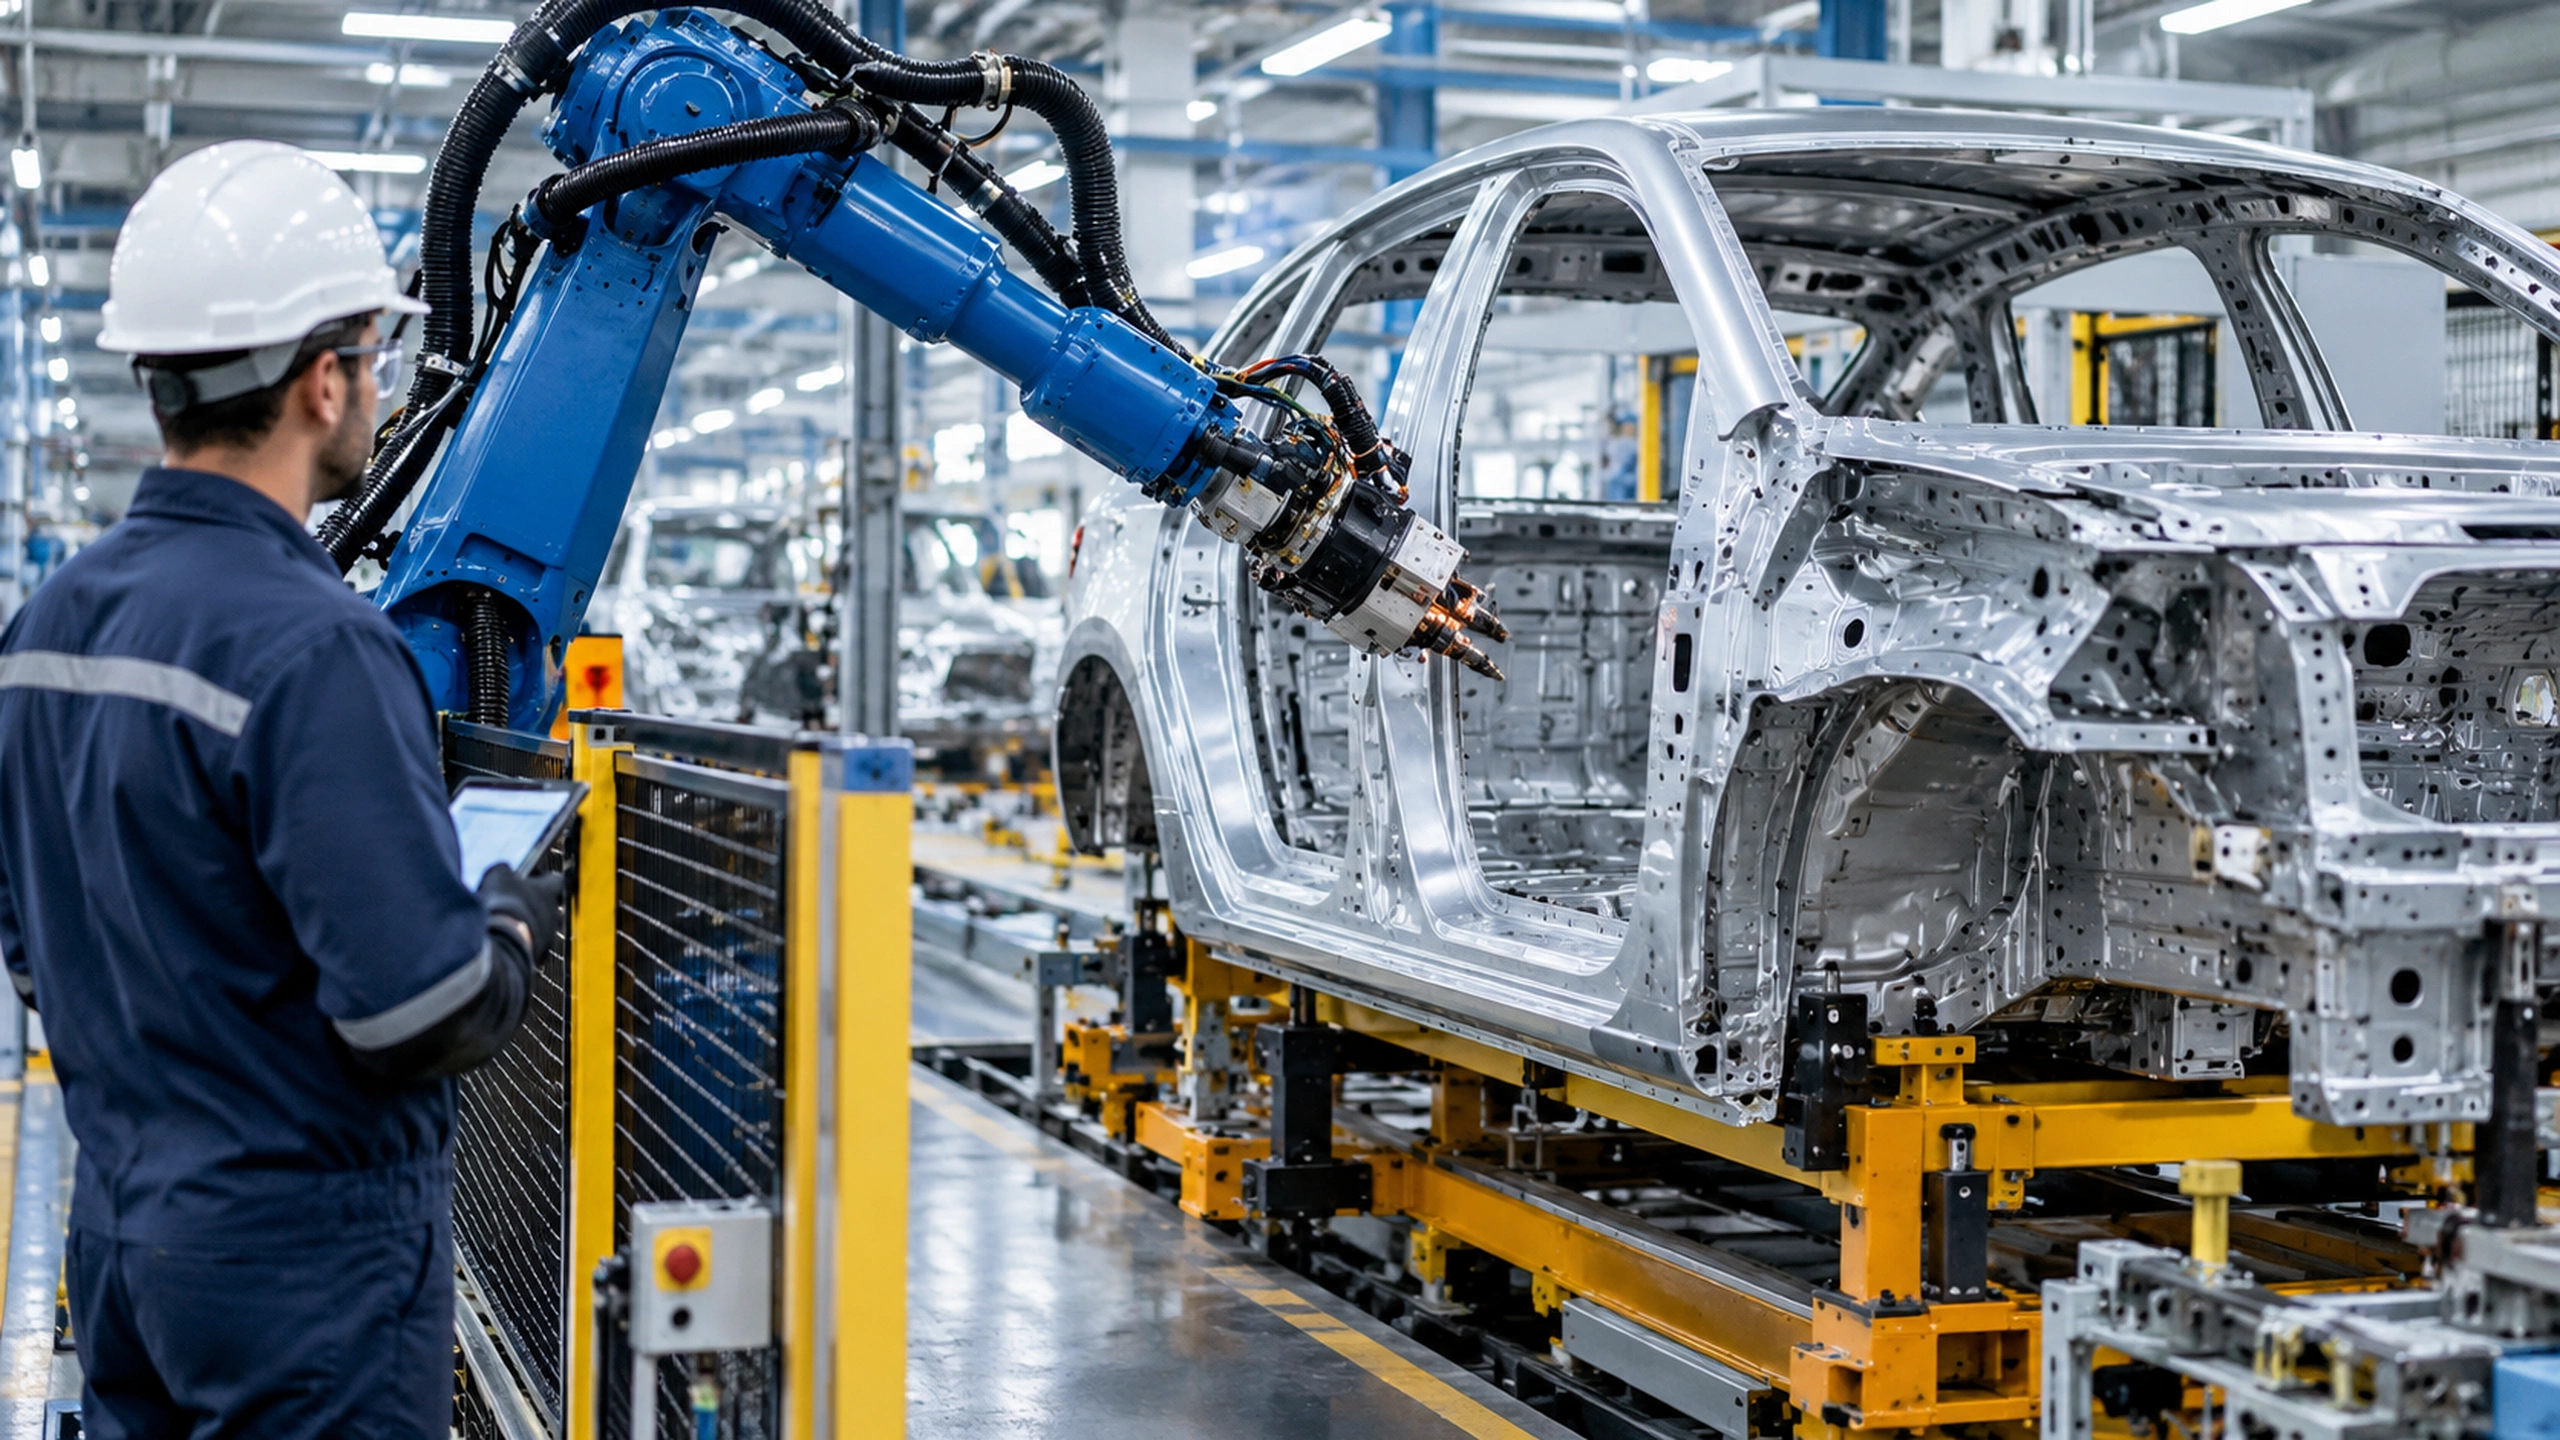
Rules and AI-generated recommendations should be evaluated against a credible baseline, such as the existing operator procedure or approved controller logic. The decision function should not bypass a programmable logic controller (PLC), safety-rated system, guarding, emergency stop, or other protective mechanism. Any physical control change requires engineering review and validation in the intended operating environment.
Human authority, protection, and fault handling
The operating design should identify who can request, approve, cancel, and override an action. Operator override and established protective functions must remain available according to site requirements. The system should define its response to loss of communications, controller unavailability, invalid permissions, unexpected motion, duplicate requests, and incomplete execution. Repeated commands must not create unintended repeated movement; command identifiers and state checks can help manage duplicate delivery.
Where autonomous execution is considered, its scope should be explicitly limited to reviewed actions and operating conditions. Actions outside that scope should be blocked or escalated. The permitted operating envelope, recovery behavior, and verification criteria should be agreed with controls engineering, manufacturing engineering, operations, and safety stakeholders before any live trial.
How to evaluate the workflow
Begin with an isolated simulation, bench setup, or controlled test that represents the chosen equipment interface and failure cases. Compare the candidate workflow with the current approved procedure under matched conditions. Include normal operation as well as stale sensor data, denied approvals, rejected commands, delayed acknowledgments, communications loss, partial movement, and disagreement between requested and observed state.
Useful measures include:
- Authorization compliance: attempted actions that passed all required permission and process checks.
- Verified action rate: eligible actions whose intended physical result was confirmed by independent observations.
- Rejected or blocked commands: counts and reasons, including invalid state, missing approval, and limit violations.
- Intervention and recovery: operator overrides, time to reach a defined safe or recoverable state, and unresolved exceptions.
- Constraint violations: any observed departure from approved process limits, reported separately from task completion.
- Traceability: completeness of linked observation, decision, approval, command, acknowledgment, and outcome records.
Report the test conditions, baseline, metric definitions, and limitations. Simulation can expose workflow gaps and compare policies under stated assumptions, but it does not establish that a real installation is safe, certified, or ready for production. A site pilot must validate the actual equipment, interfaces, interlocks, network behavior, and operator procedures.
Integration considerations
Implementation may involve sensors, edge devices, a gateway, a PLC or other controller, a manufacturing execution system (MES), and plant-level applications. The integration design should document which component owns each state, how timestamps and equipment identifiers are mapped, what happens during network interruption, and where event and approval records are retained. Compatibility with a specific controller or enterprise system must be confirmed rather than assumed.
OEMNex’s Physical AI and AIoT approach provides a way to structure identification, sensing, decision support, and authorized action as distinct functions. The appropriate architecture and execution mode depend on the plant’s requirements and the capabilities verified during technical assessment.
Discuss an authorized-action workflow
Discuss your application with OEMNex to define the equipment boundary, action target, operating constraints, approval path, available observations, and evidence needed to verify completion. A useful first step is to select one bounded manufacturing task and agree on how success, rejected actions, exceptions, and recovery will be measured.
Contact OEMNex