
Connect Plant Data with Enterprise Workflows
Integration connects physical observations and AI-supported decisions with the systems already used across an original equipment manufacturer (OEM) vehicle plant. A vehicle body, torque tool, robotic cell, conveyor, or inspection station may generate useful events, but those events only support operations when they can be associated with the correct asset, production order, station, and time.
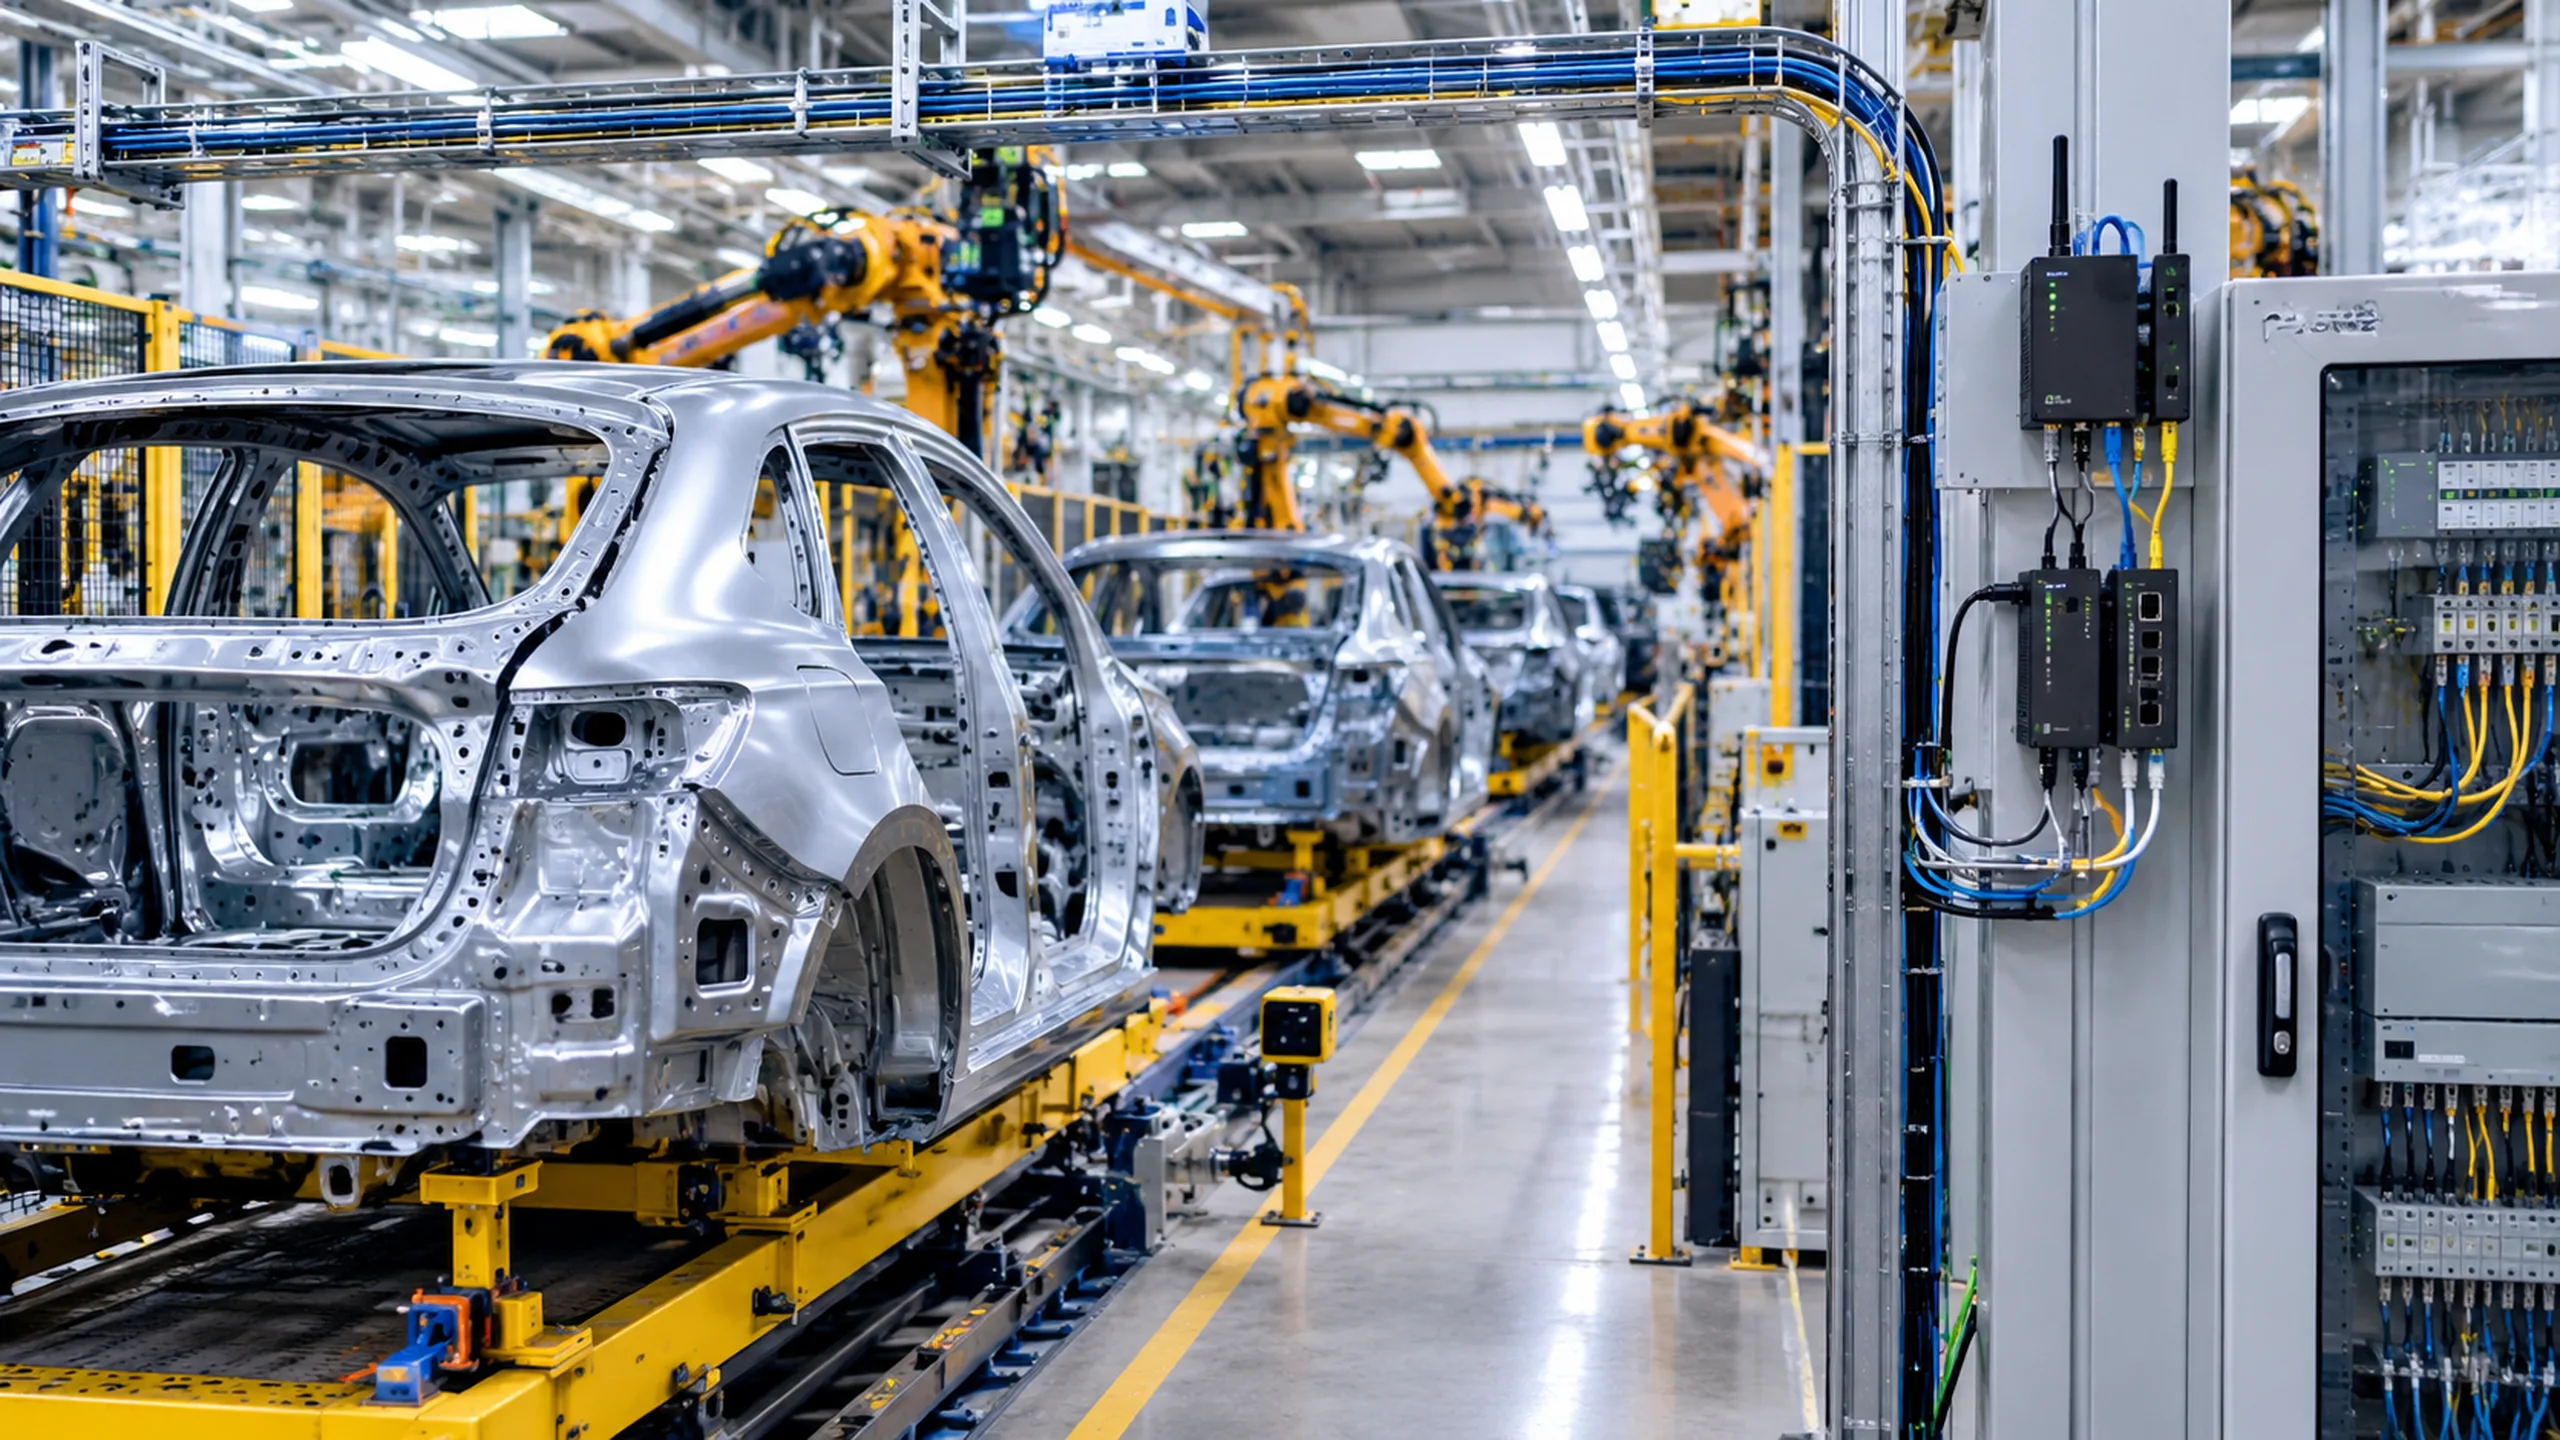
OEMNex focuses on Physical AI and Artificial Intelligence of Things (AIoT) applications for OEM vehicle manufacturing. Integration design should define data ownership, interfaces, deployment responsibilities, and behavior when a system or network is unavailable. The appropriate design depends on the plant's existing architecture, production requirements, approved access paths, and the capability being evaluated.
A practical integration scope begins with one workflow, such as linking a body-in-white inspection event to its vehicle identifier and manufacturing execution record. It then identifies the source systems, required data, users, decision points, and the evidence needed to verify that the workflow operates as intended.
Map the Systems Involved
An integration plan should identify each system's role before selecting interfaces or deployment locations. The following systems may be relevant in an automotive manufacturing environment, depending on the plant's architecture:
- Enterprise resource planning (ERP) manages business resources, purchasing, inventory, and production-related business records.
- Manufacturing execution systems (MES) coordinate production orders, work-in-process, routing, station activity, and manufacturing genealogy.
- Warehouse management systems (WMS) manage material storage, replenishment, picking, and warehouse movements.
- Computerized maintenance management systems (CMMS) manage equipment records, maintenance requests, work orders, and service history.
- Supervisory control and data acquisition (SCADA) systems provide supervisory visibility into industrial processes, equipment states, and alarms.
A connected workflow may consume equipment observations, associate them with a vehicle or production station, and provide a reviewed event to an MES, CMMS, or analytics application. Not every system needs a direct connection. Integration can use an approved intermediary or data service where that better fits security, maintainability, and plant standards.
The system map should show the owner of each data source, the direction of data exchange, the required response time, and whether an interface is read-only or permits writes. Access to production control systems should be limited to the functions explicitly approved for the use case.
Define Data Contracts Before Connecting Systems
A data contract defines how systems identify, interpret, exchange, and reject records. Agree on the contract with plant operations, manufacturing engineering, IT, and controls stakeholders before implementation.
- Identifiers: specify the canonical vehicle, component, tool, station, or equipment ID and the rules for resolving mismatches.
- Time: distinguish event time from ingestion time, define the time zone and clock-synchronization expectations, and document how delayed messages are handled.
- Event mapping: define source event names, units, enumerations, status values, and how plant-specific codes map to the receiving system.
- Data quality: specify required fields, valid ranges, quality flags, duplicate handling, and the destination for rejected or incomplete records.
- Versioning: record interface and schema versions so changes can be reviewed and tested before release.
- Auditability: retain relevant event IDs, source references, processing outcomes, and decision records according to the organization's retention and access policies.
For example, an inspection event should preserve the vehicle or component identifier, station identifier, event timestamp, inspection result, measurement units where applicable, source device, and quality status. If the identifier is missing or the timestamp is invalid, the integration should route the record for defined handling rather than silently associating it with the wrong vehicle.
Choose a Deployment Arrangement That Fits the Plant
Deployment location affects latency, availability, data movement, maintenance, and ownership. Edge processing, a customer-managed server, private hosting, and cloud services are possible architectural patterns, not a statement that every option is available for every OEMNex implementation.
- Edge deployment places selected processing close to equipment or a production cell. It can reduce dependence on continuous upstream connectivity, but requires site-level power, network, physical security, update, and service planning.
- Customer-managed server deployment can keep processing within an organization's existing facility or data center. The customer and implementation team need clear responsibilities for operating system maintenance, capacity, backups, monitoring, access, and recovery.
- Private hosting may provide a controlled environment managed under an organization's infrastructure and security policies. Confirm network paths, identity management, support boundaries, and data residency requirements.
- Cloud deployment can support centralized services across facilities when permitted by the plant's security, latency, connectivity, and data-governance requirements. The design must specify what happens when the plant loses its connection to remote services.
The decision should account for the task's response-time needs, volume and sensitivity of data, network reliability, operating hours, maintenance windows, and the skills available to support the deployment. Compare the full operating responsibility, including installation, monitoring, patching, backups, incident response, data export, and ongoing support, rather than comparing hosting fees alone.
Keep Production Workflows Reliable and Secure
Automotive production depends on predictable equipment behavior and traceable records. Integration design should describe normal operation as well as degraded conditions, including network interruption, delayed messages, unavailable enterprise services, device restart, and rejected records.
- Buffer and replay: define which events can be stored locally, how long they can be retained, and how replay avoids creating duplicate records after connectivity returns.
- Recovery: specify restart behavior, reconciliation steps, and how operators can identify missing or delayed data.
- Access boundaries: apply least-privilege access, separate read and write permissions, and document the systems and accounts permitted to exchange data.
- Logging: record interface errors, rejected messages, configuration changes, deployment versions, and administrative activity needed for troubleshooting and audit.
- Updates and rollback: assign responsibility for testing, scheduling, approving, deploying, and reversing software or configuration changes.
- Physical control boundaries: keep AI recommendations and supervisory requests distinct from validated low-level equipment control and independent protective functions. A software demonstration does not establish that a physical installation is safe or certified.
If a connected function can propose or initiate an equipment action, the workflow must define authorization, operating limits, timeout behavior, manual override, and how the resulting physical state will be checked. A command acknowledgment alone does not prove that the intended equipment action occurred.
Validate Interfaces Before Production Release
A connector should be described as tested only when test records support that claim. For each proposed or existing interface, record the source and destination systems, interface version, authentication method, data mapping, access mode, installation dependencies, and validation status. Distinguish a planned interface from one exercised in a controlled test or commissioned at a customer site.
A staged validation plan can include:
- Requirements review: confirm the workflow, system owners, source data, access approvals, response-time needs, and acceptance criteria.
- Interface testing: check valid records, missing fields, malformed messages, duplicate events, timestamp mismatch, out-of-order delivery, and unknown identifiers.
- Failure and recovery testing: interrupt connectivity, restart relevant services, simulate destination unavailability, and verify buffering, replay, alerting, and reconciliation.
- Security review: verify account permissions, network boundaries, credential handling, logging, and update procedures against the customer's requirements.
- Operational acceptance: have plant and IT/OT owners confirm the workflow, exception handling, support process, and rollback plan before the agreed release.
Acceptance criteria should be measurable and specific to the use case. Examples include the proportion of required events correctly associated with the right vehicle, the number of duplicate or rejected records, event delivery delay, recovery time after a planned interruption, and the completeness of audit records. Define the measurement window, denominator, test conditions, and exclusions before testing.
Example: Trace an Inspection Event to a Vehicle Record
Consider a proposed workflow at a vehicle assembly plant. A station captures an inspection result for a vehicle body. The integration layer validates the station and vehicle identifiers, normalizes the timestamp and result fields, and forwards an accepted event to the approved manufacturing record system. If a required identifier is missing or the destination is unavailable, the record is flagged and held for defined recovery or review.
This example is an implementation pattern, not a claim that a particular connector has been tested or deployed. A pilot should confirm that identifiers remain consistent across systems, events arrive within the required window, rejected records are visible to the responsible team, and recovery does not create false or duplicate production history.
Plan Commissioning, Ownership, and Ongoing Support
Deployment is not complete when the software starts. Commissioning should confirm the installed configuration, data paths, access permissions, monitoring, recovery procedures, and the responsibilities of each party. Document site prerequisites such as network routes, firewall approvals, power, mounting, environment, maintenance access, software versions, and required change windows.
Before handoff, agree on who owns interface changes, schema updates, credentials, alerts, backups, incident escalation, and support after production release. Document rollback conditions and the process for returning to the previous approved configuration. Where an interface depends on a third-party system or supplier, identify that dependency and the party responsible for maintaining it.
A deployment record should include the tested configuration, test results, known limitations, acceptance decisions, unresolved issues, and the date and owner of approval. This record helps future teams assess changes without assuming that a previously tested interface remains compatible after an upstream system update.
Discuss Your Integration Requirements
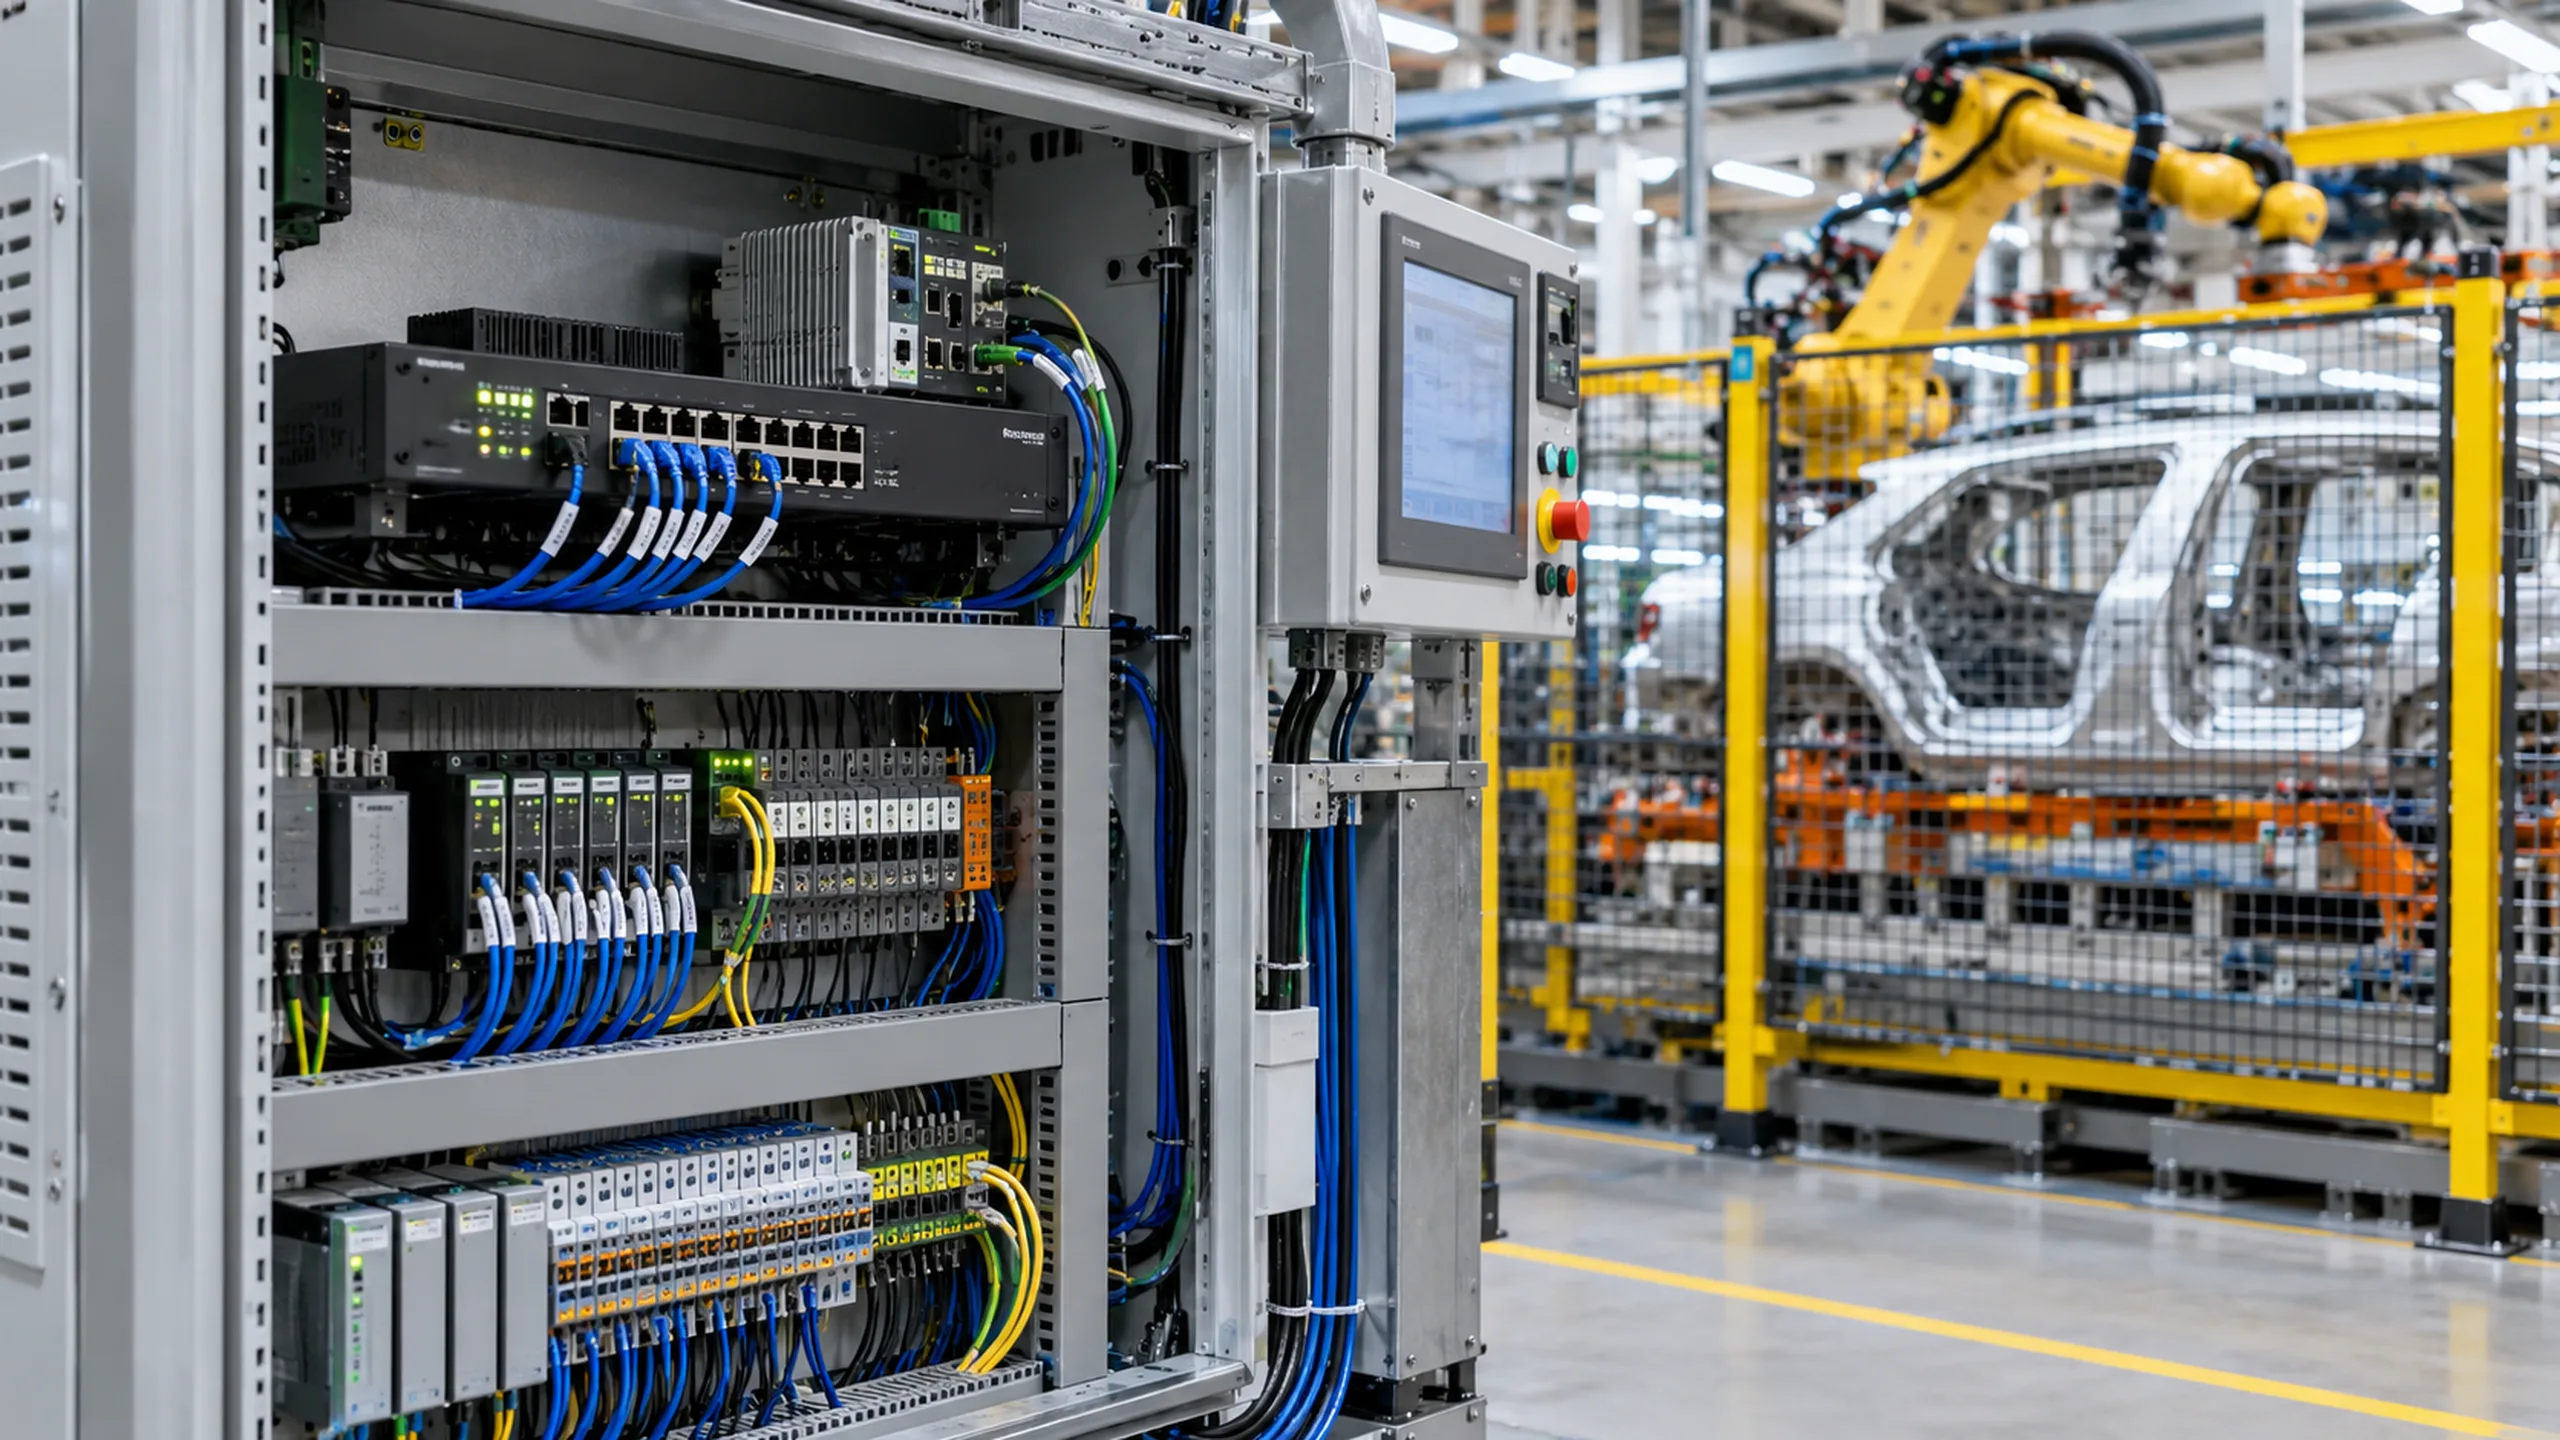
OEMNex can use an initial requirements discussion to map the target workflow, source and destination systems, data contract, deployment constraints, and validation plan. Bring a high-level plant architecture, representative non-sensitive event records, interface documentation, and the acceptance criteria that matter to operations. Do not share credentials, confidential production data, or sensitive network details through an unapproved channel.