
The Physical AI Action Engine for OEM Vehicle Manufacturing
The Physical AI Action Engine connects an approved operational decision to a defined physical response. In an OEM vehicle plant, that response might involve requesting a robot inspection, authorizing a material handling step, or adjusting equipment within an engineered operating range. Each action needs a known target, a permitted command path, explicit limits, and evidence of the resulting equipment or process state.
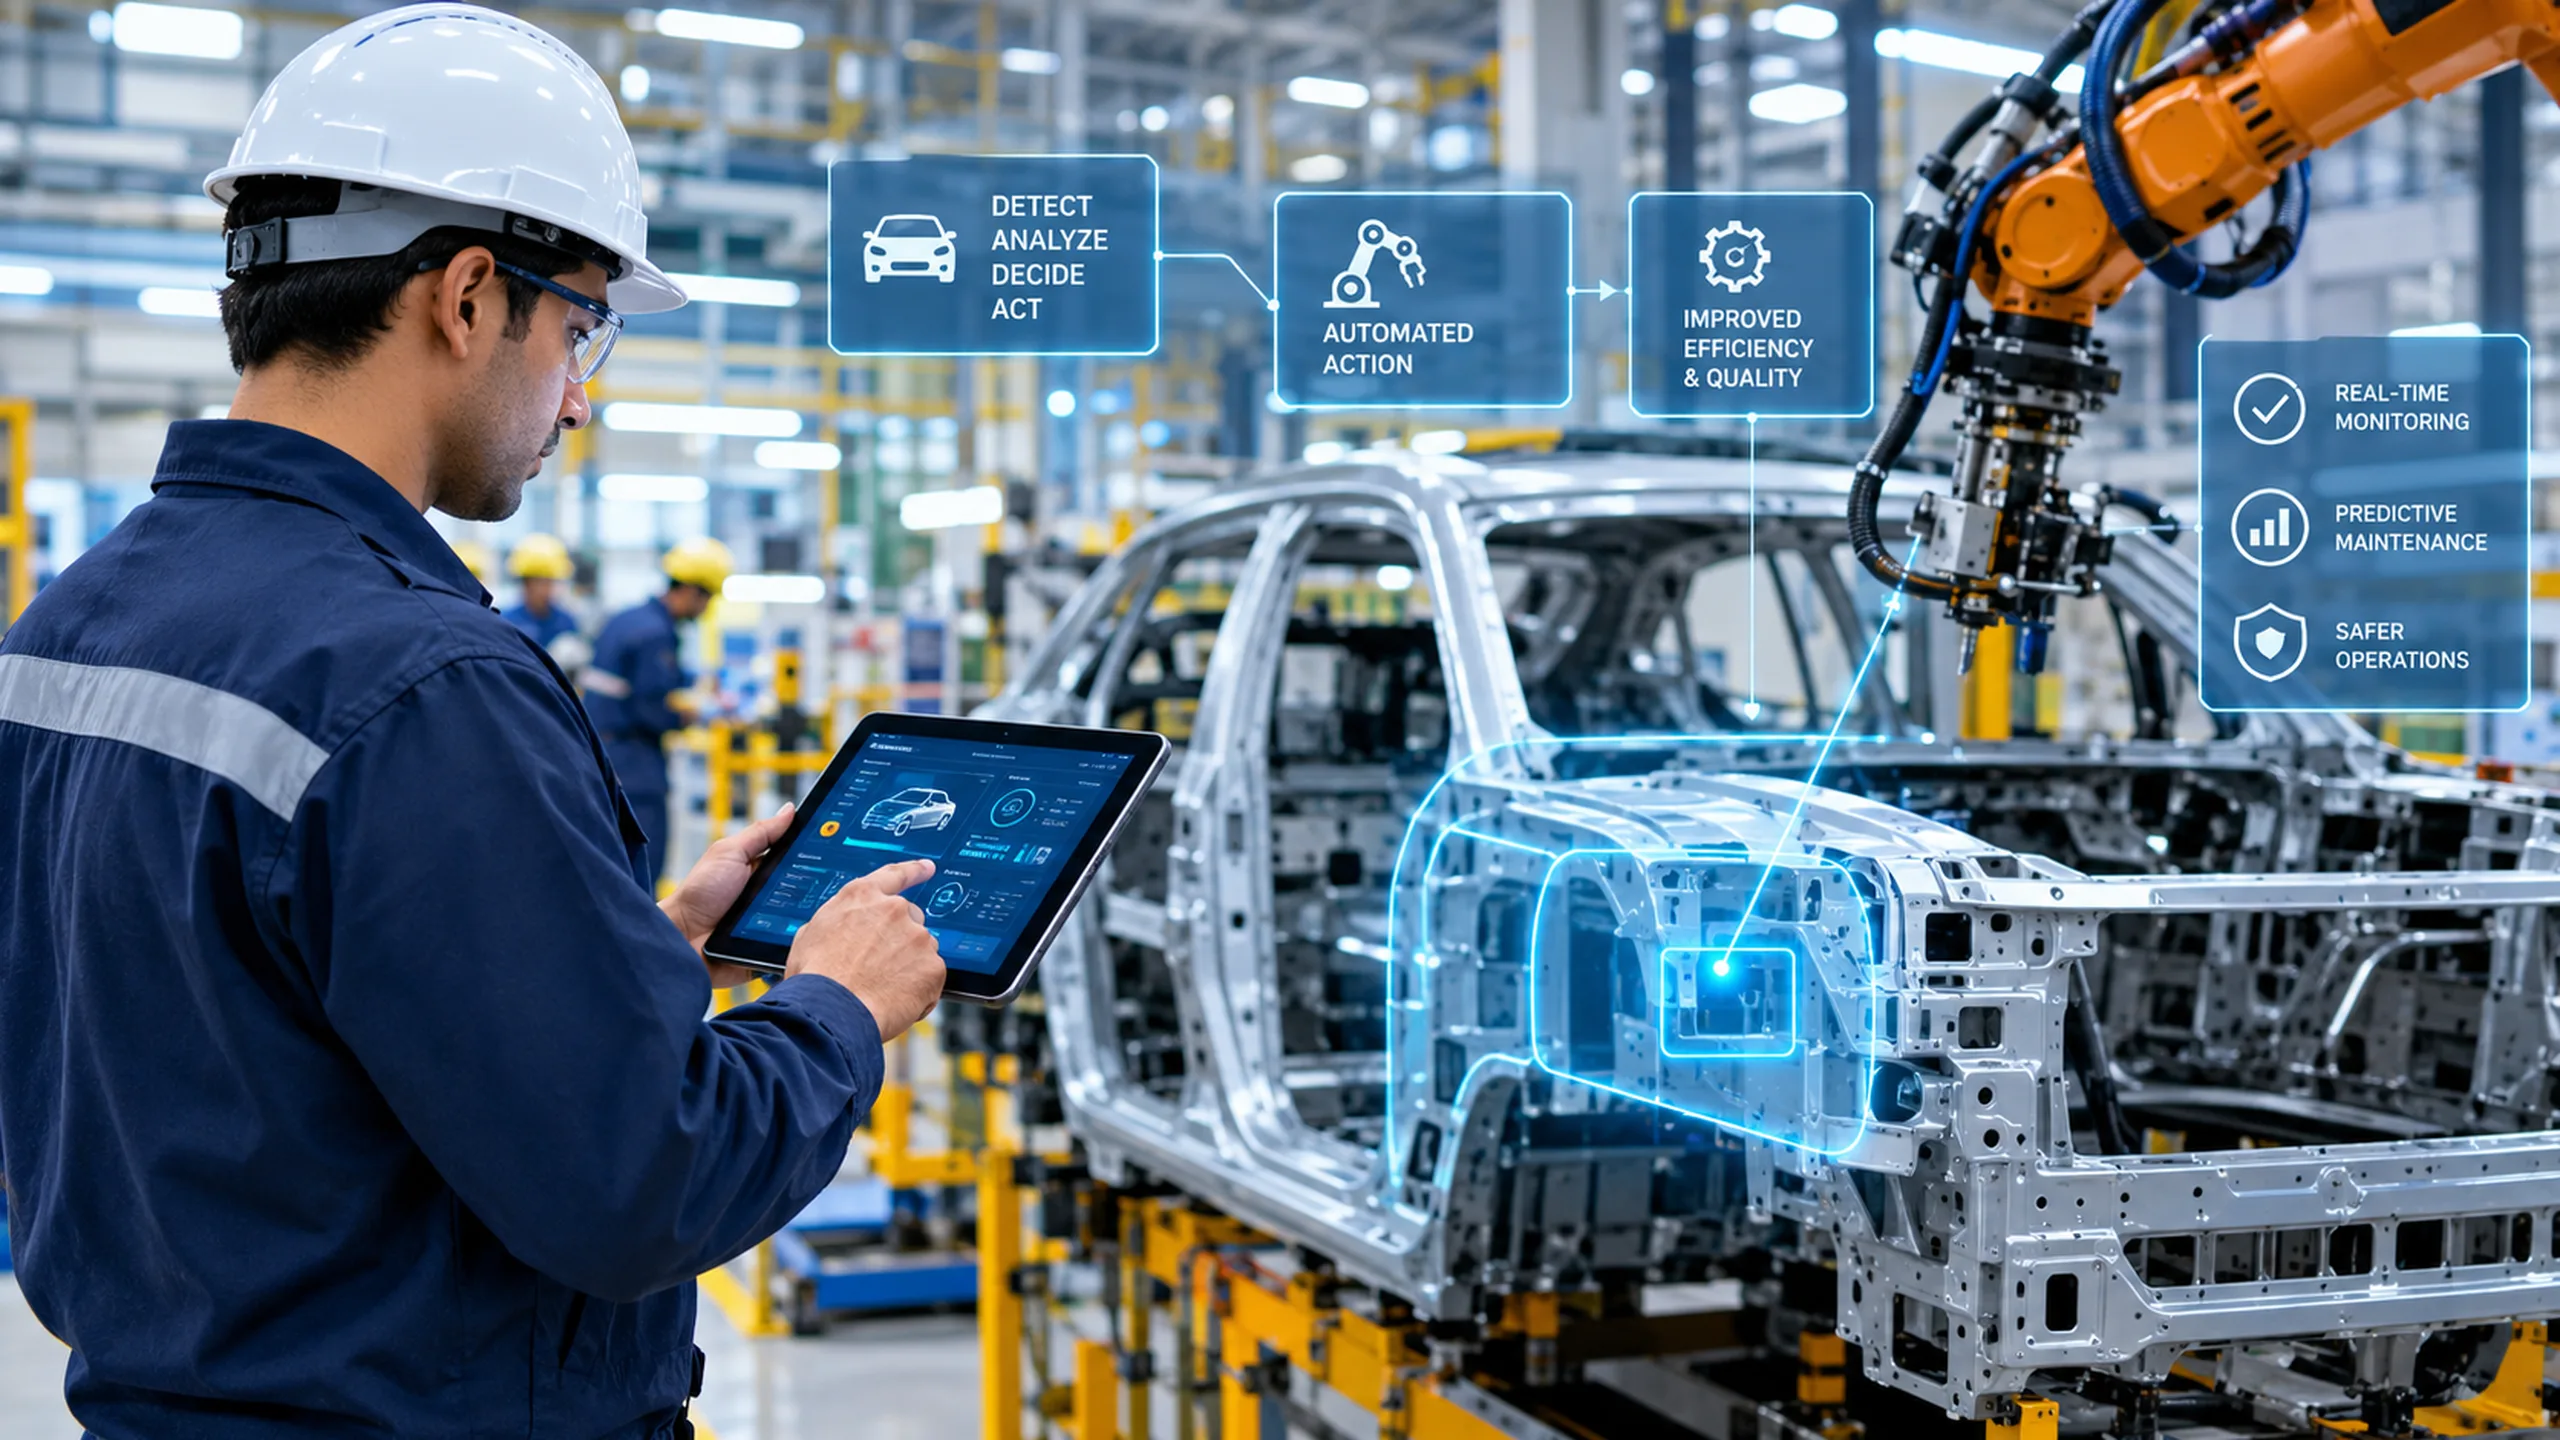
From AI Decision to Physical Execution
An action workflow begins with current observations and a decision from the AI Decision Engine or an established control rule. The action layer checks whether the target is correctly identified, the data is sufficiently current, the requested operation is allowed, and the relevant equipment is available. It then routes an approved command through the appropriate gateway, controller, or machine interface.
For example, a vision-based quality workflow may flag a vehicle body panel for a closer inspection. The system can create an inspection request or, where the integration has been engineered and authorized, dispatch a robot to a defined inspection position. The request itself does not prove that the inspection occurred. Position, sensor, or inspection records must confirm the outcome.
Physical Actions in Vehicle Manufacturing
The suitable action depends on the production cell, equipment, process boundary, and validated interface. Potential workflows to assess include:
- Robotic inspection: send an approved inspection mission to a robot or vision station and record whether the target and inspection step were completed.
- Material handling: request or authorize movement of a component, fixture, or container when identity, destination, access conditions, and equipment availability have been checked.
- Equipment adjustment: submit a bounded setpoint or operating adjustment through an approved control interface, subject to the machine’s existing limits and protective functions.
- Quality containment: route a suspected nonconforming part for review, reinspection, or a validated hold process rather than allowing an unverified AI result to trigger an unrestricted action.
These are application patterns, not claims that every workflow or equipment interface is currently supported by OEMNex. The actual action set must be agreed with the plant and verified against its controls, safety requirements, and operating procedures.
Choose the Right Execution Mode
Not every decision should directly control equipment. Select the execution mode according to risk, evidence, and the level of integration that has been validated.
- Human-mediated: The system presents a recommendation or creates a work request. A qualified employee performs the action and records the result.
- Human-approved: The system prepares a specific command, but an authorized operator or supervisor must approve it before dispatch.
- Bounded autonomous: A validated system may execute a narrowly defined action within approved limits, with monitoring, exception handling, and a documented fallback path.
Autonomous execution should be considered only after the action, operating envelope, failure behavior, and verification method have been reviewed. Existing machine safety functions and independent protective controls must remain authoritative.
The Command and Control Path
A practical action path separates the decision from execution and preserves a record at each stage:
- Propose: identify the target asset, requested action, reason, decision ID, and relevant observations.
- Authorize: check identity, user or service permissions, operating mode, machine availability, and required approval.
- Validate: confirm that the command is well formed, current, within permitted limits, and not a duplicate request.
- Dispatch: send the command through the configured gateway, controller, actuator, or robotic interface.
- Acknowledge: record whether the receiving system accepted or rejected the command. An acknowledgment is not proof of physical completion.
- Verify: compare subsequent sensor readings, equipment state, robot position, or inspection records with the intended result.
- Recover or escalate: handle timeouts, communication loss, partial execution, rejection, or disagreement between commanded and observed state.
The implementation may depend on programmable logic controllers (PLCs), robot controllers, drives, actuators, industrial gateways, and supervisory control interfaces. Compatibility, timing, command semantics, and feedback availability must be checked for each equipment type. A work-order request or enterprise-system update is not the same as direct physical control.
Safeguards, Permissions, and Exceptions
Physical actions can affect personnel, product quality, equipment, and production continuity. The design should define who or what may request an action, which roles can approve it, and which conditions must block execution. Depending on the cell, safeguards may include interlocks, restricted operating zones, equipment-specific limits, manual override, and independent safety systems.
The action workflow must also define what happens when sensor data is stale, the target identity is uncertain, a command is rejected, a response arrives late, or connectivity is lost. The system should not retry a potentially non-idempotent action blindly. It should use a documented timeout and recovery policy, reconcile the actual equipment state, and escalate to an authorized person when safe continuation cannot be established. AI software does not replace machine risk assessment, commissioning, or required safety validation.
Verify Outcomes, Not Just Commands
A useful action record links the initiating observation and decision to the authorization result, command, acknowledgment, and independent outcome evidence. A minimum record may include asset ID, event time, ingestion time, decision ID, command ID, operator or service identity, model or rule version, command status, observed state, and quality flags. Timestamps, units, and event ordering should be consistent across connected systems.
Evaluation should measure both the operational objective and the failure cases. Depending on the workflow, measures may include verified action rate, command rejection rate, time from approval to completion, failed or partial execution, manual interventions, constraint violations, recovery time, and disagreement between commanded and observed states. Compare results with a documented baseline and test normal operation as well as communication faults, delayed messages, stale observations, and unavailable equipment.
Integration and Deployment Considerations
Before implementation, map the selected action to the relevant production cell, controller interface, network path, asset records, and plant systems. Establish data ownership, access controls, command logging, software and configuration versioning, and responsibility for maintenance. Test the workflow in a controlled environment before any live equipment is allowed to respond.
A pilot should begin with one clearly bounded workflow and agreed acceptance criteria. Confirm that observations represent the actual operating state, that authorization and rejection paths behave as intended, and that outcome checks can distinguish success from an accepted command that never completed. Record limitations and untested interfaces; do not treat a software demonstration or simulated protective logic as proof of safe deployment.
How the Action Engine Fits the Engine Architecture
The Physical AI and AIoT Engines Architecture describes how identity, sensing, decisions, authorized commands, and feedback relate. The AI Decision Engine provides the decision or action proposal; the Physical AI Action Engine governs the path from an approved proposal to equipment execution and outcome verification. Implementation details are covered in Physical Action and Control Technologies. For safeguards and access considerations, see Cybersecurity and Physical Action Safeguards.
Discuss an Automotive Manufacturing Workflow
Discuss a specific vehicle manufacturing workflow with OEMNex. Identify the target equipment or material, the decision that should initiate action, the approval authority, the available control interface, and the evidence needed to verify completion. This provides a practical basis for assessing integration requirements, constraints, and pilot acceptance criteria.